IT infrastructure for growing businesses

IT that stays out of your way.

We assess, build, secure, and maintain the systems behind everyday work — without turning technology into another management problem.

Explore services ↘
See what breaks first ↓
IT engineer labeling cables in an unplanned office network closet
REAL CONDITIONS / BEFORE STANDARDIZATION
Problem / reality

The expensive part is rarely one broken device.

It is the accumulation of undocumented changes: shared passwords, improvised cabling, cloud accounts without clear ownership, and backups nobody has tested. We turn that uncertainty into a visible, maintainable system.

Vulnerability is not only a coding problem. It often begins with missing ownership, incomplete documentation, and decisions made in isolation.
  1. 01Downtime from a single unmanaged dependency
  2. 02Access that remains after roles or staff change
  3. 03Slow work caused by fragmented cloud and network tools
Services / clear starting points

Five ways to make everyday IT more dependable.

Pricing is a practical starting point for a newly established US provider. The final scope depends on users, devices, locations, platforms, and migration complexity.

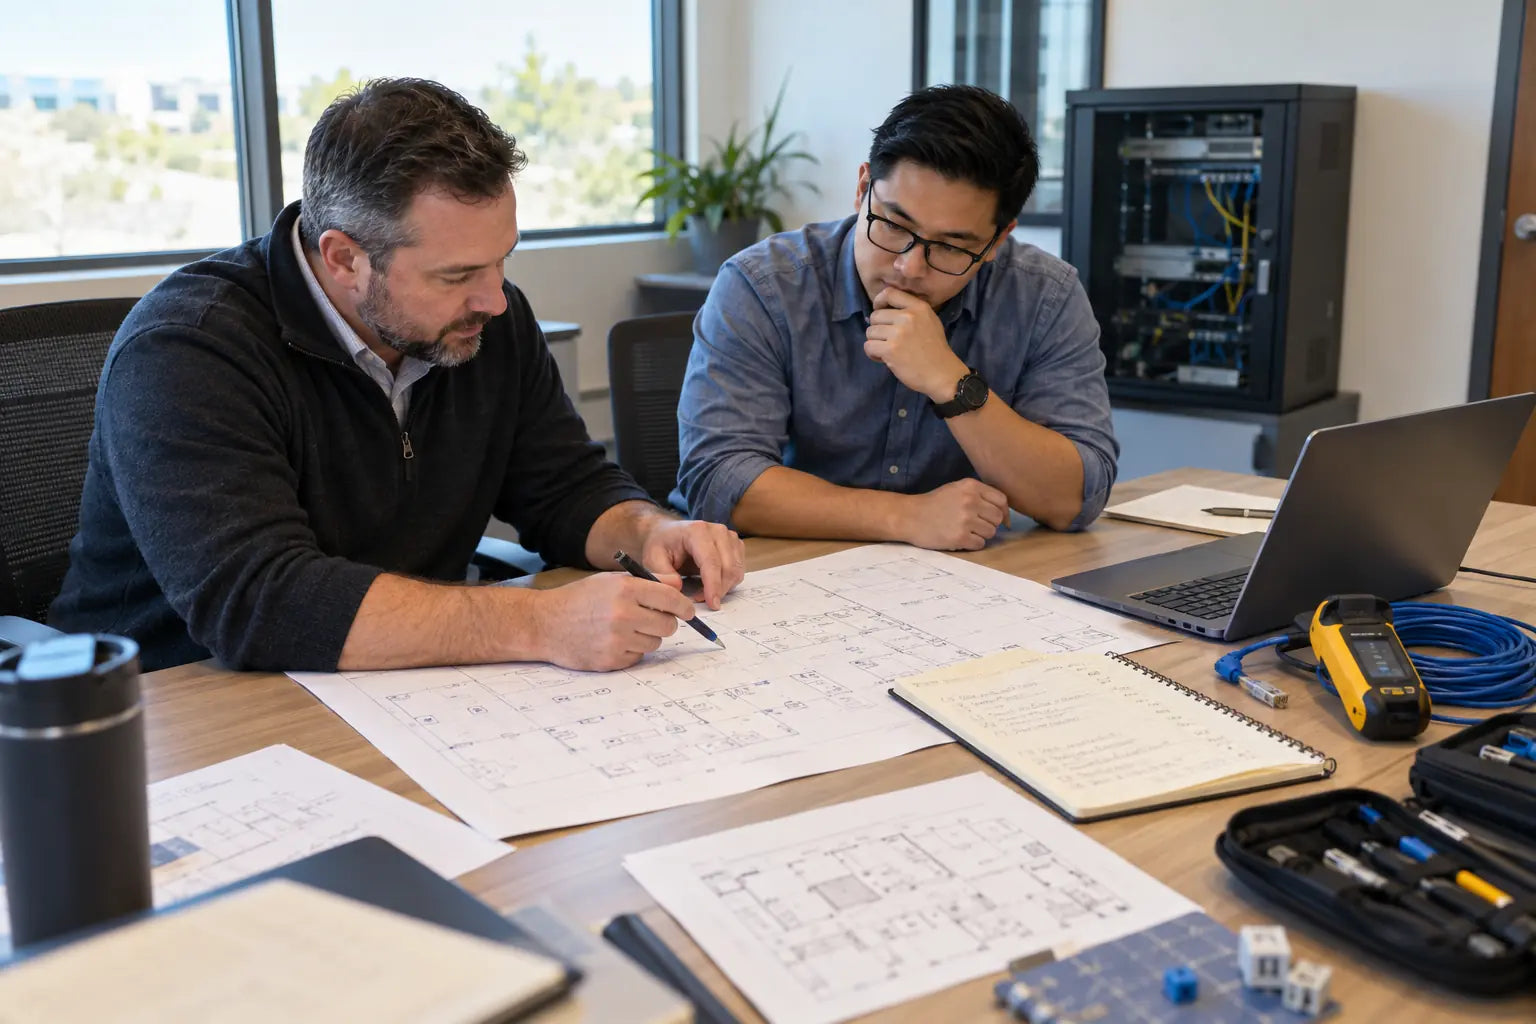
Two IT consultants reviewing network plans and equipment in an office
01 / Assessment

IT Assessment & Technology Plan

A complete review of your current IT environment, including vulnerabilities, bottlenecks, ownership gaps, and a prioritized 12-month modernization roadmap.

  • Fixed assessment scope
  • Delivery within 5 business days
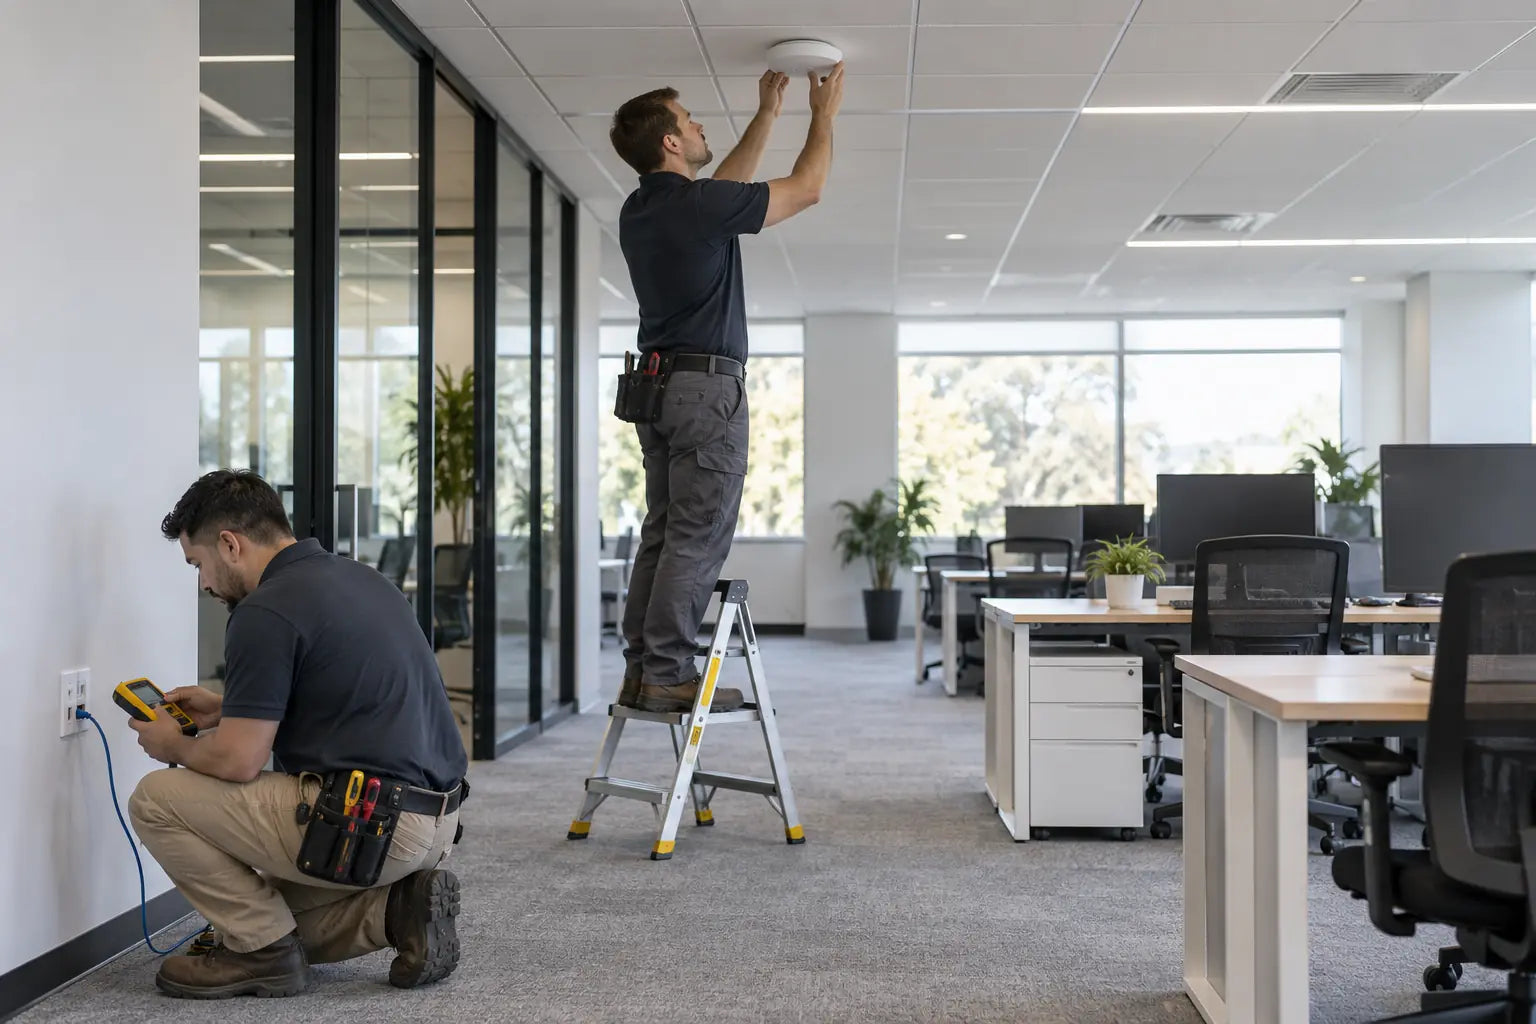
Technicians installing and testing office network equipment
02 / Network

Business Network Setup & Optimization

Design and configuration of resilient wired and Wi-Fi infrastructure with seamless roaming, traffic separation, and priority for voice and video work.

  • Coverage and equipment plan
  • Configuration and on-site validation
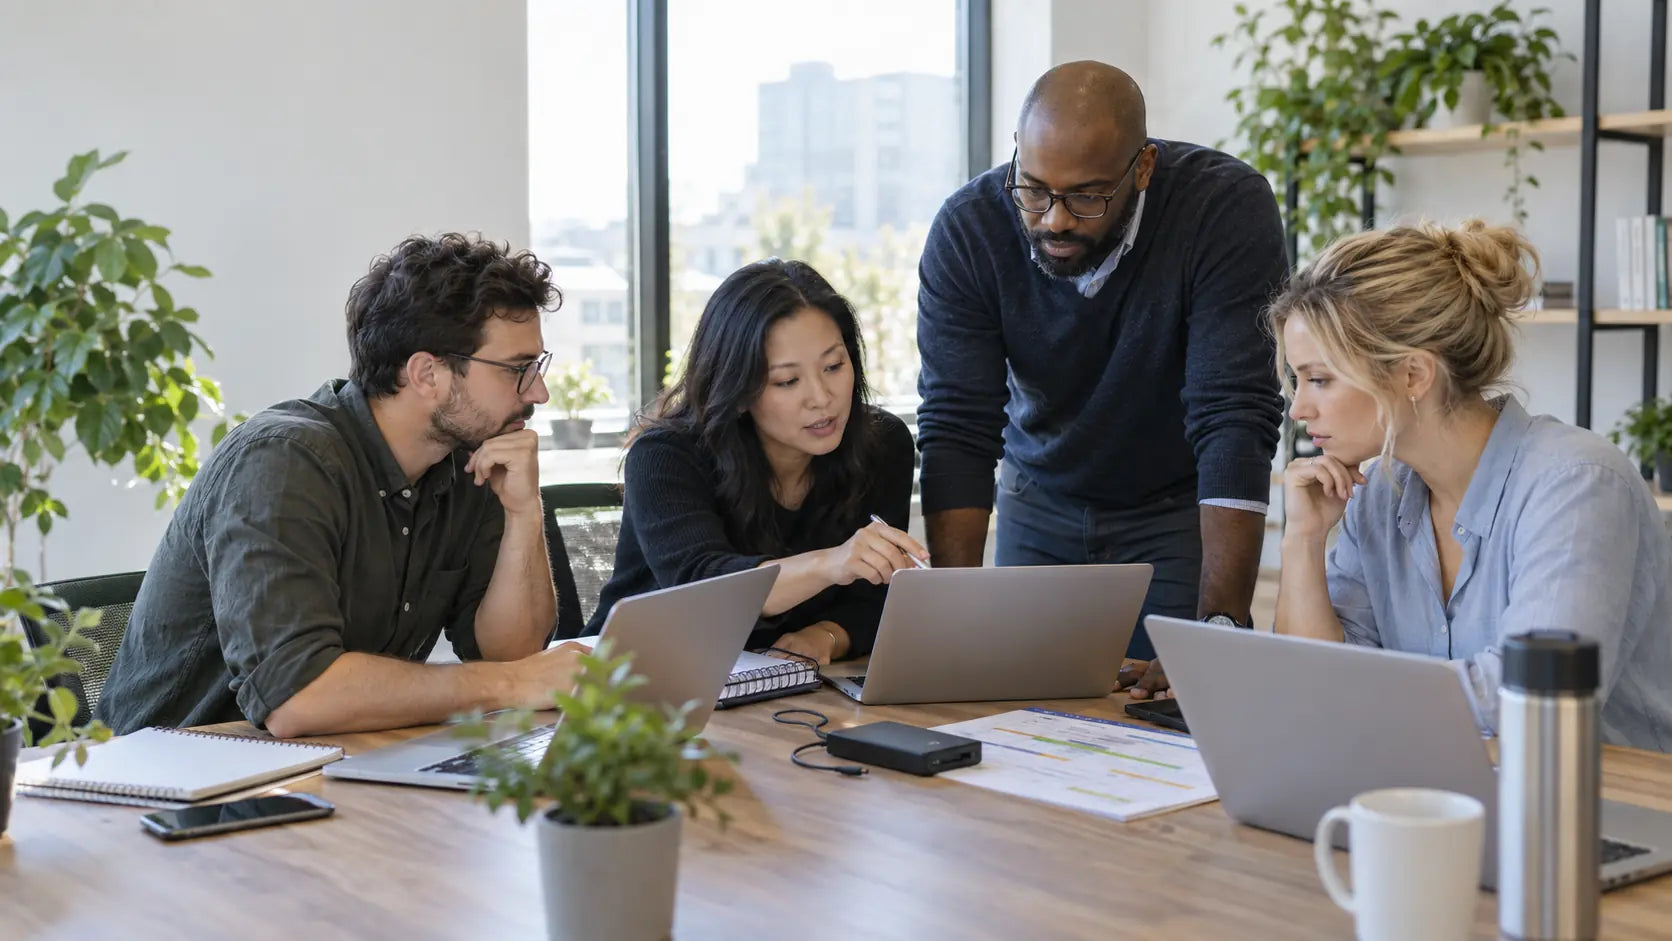
Business team planning a cloud workspace migration around a meeting table
03 / Cloud

Cloud Workspace Setup & Migration

Structured migration of data, email, and work applications to AWS, Microsoft 365, or a private cloud, sequenced to minimize disruption to daily operations.

  • Migration sequence and ownership
  • Access and continuity checks
Engineer connecting a secure network appliance on a workbench
04 / Protection

Cybersecurity Review & Protection Setup

Layered protection covering encryption, multi-factor authentication, anti-phishing controls, DDoS readiness, access policies, and backup configuration.

  • Protection baseline
  • Prioritized remediation list
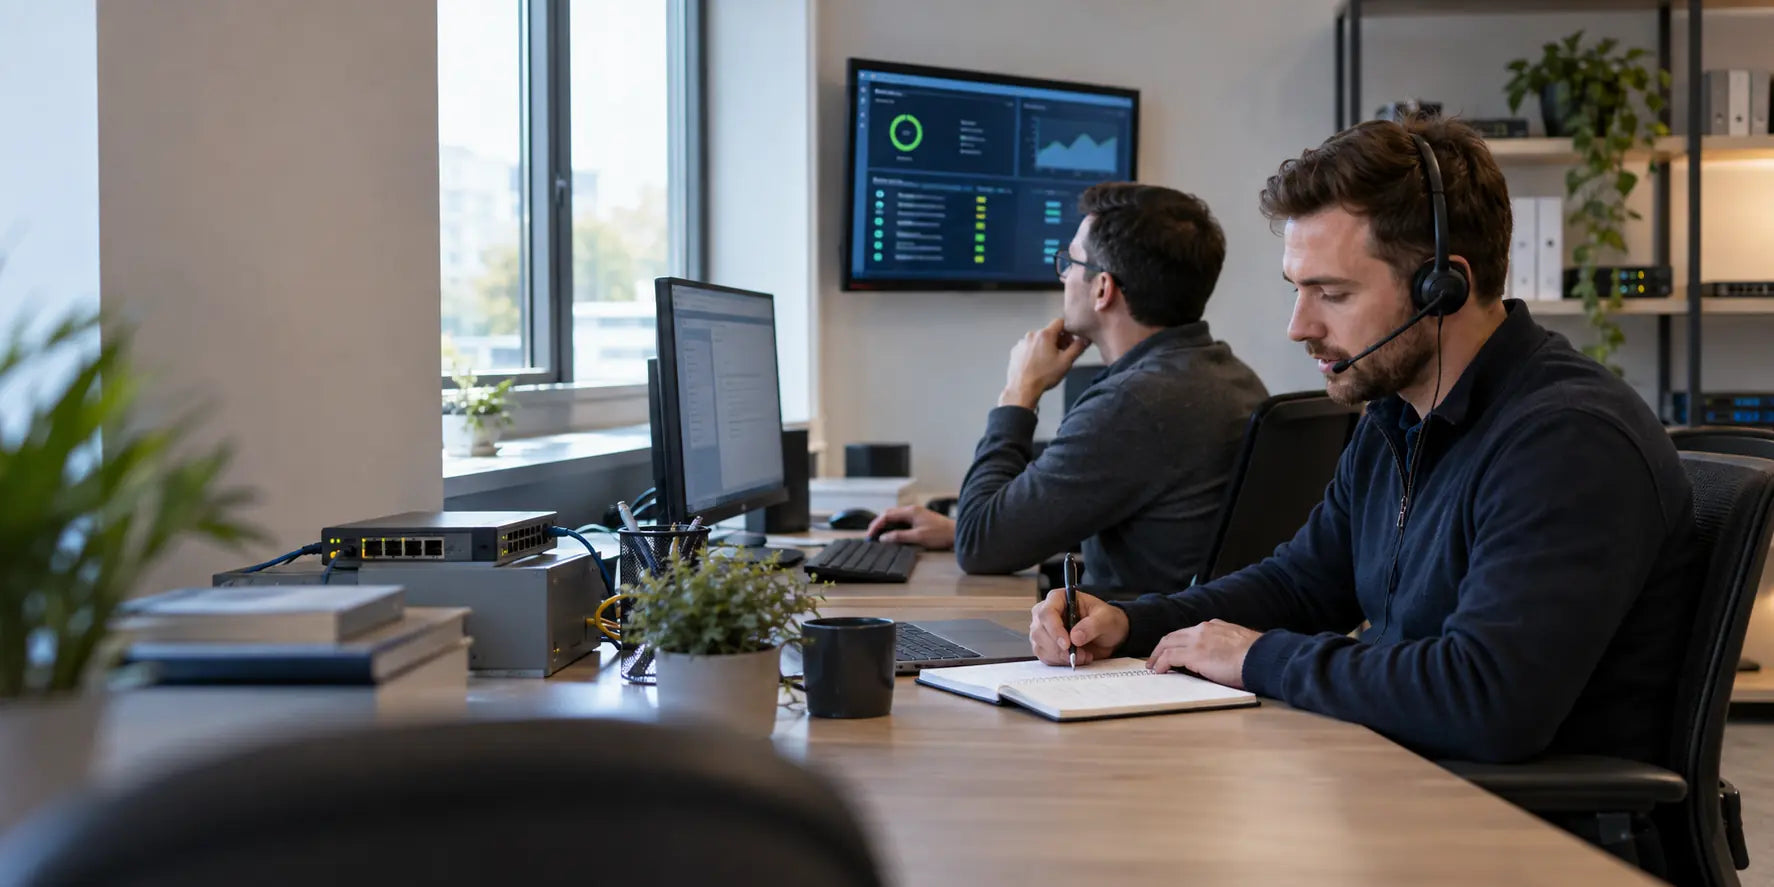
IT support engineers monitoring and documenting an incident
05 / Support

Managed IT Support & Maintenance

Ongoing infrastructure oversight, preventive maintenance, issue triage, and coordinated support designed around your operating hours and existing systems.

  • Defined support coverage
  • Recurring maintenance plan
Reliability targets

Defined outcomes, not vague promises.

Targets are written into the selected scope and verified against the systems we can actually control.

Technician checking backup power equipment and documenting results
POWER / BACKUP / RECOVERY CHECK
< 15 minTarget initial response for covered incidents under the selected support plan.
99.99%Cloud-service availability target where the chosen platform and scope support it.
0 bytesRecovery objective supported by verified backup, retention, and restore controls.

These are service targets and recovery objectives, not historical performance claims or blanket guarantees for third-party platforms.

Operating method

Change the system without losing the day.

Work is sequenced around risk, business hours, and clear decision points. Each phase leaves something concrete behind.

Organized IT installation tools, plans, labels and cable testing equipment
FIELD KIT / PLAN BEFORE CHANGE
01

Observe

Inventory users, devices, platforms, access, recurring issues, and dependencies.

02

Prioritize

Separate immediate risks from improvements that can be scheduled and budgeted.

03

Implement

Use controlled windows, checkpoints, documentation, and rollback planning.

04

Verify

Confirm access, performance, backups, ownership, and the next maintenance interval.

Continuity blueprint

What happens before, during, and after an IT problem.

01BEFORE

Prevent

Secure defaults, documented ownership, patch planning, tested backups, and clear escalation paths reduce avoidable incidents.

Baseline controls
02DURING

Stabilize

Establish impact, preserve useful evidence, restore essential access, and communicate the next practical action.

Incident sequence
03AFTER

Improve

Use recurring issues and business changes to guide measured network, cloud, security, and maintenance priorities.

Next-cycle plan
Documentation handoff

Your infrastructure should not live in someone else's memory.

Each project closes with documentation matched to the work completed, so ownership and the next decision remain clear.

DOCUMENT / 01

System map

A readable view of the devices, services, dependencies, and owners included in the completed scope.

Current state
DOCUMENT / 02

Access register

A practical record of administrative ownership, role boundaries, and access changes that need periodic checking.

Accountability
DOCUMENT / 03

Recovery checklist

Plain-language steps for backups, restoration priorities, and the people responsible for escalation.

Continuity
DOCUMENT / 04

Next actions

A prioritized list separating completed work, accepted risks, maintenance items, and future improvements.

Forward plan

The exact documents depend on the selected service and written project scope.

Quiet office meeting table prepared for a project discussion
Start with a useful brief

Tell us what needs to work better.

Select the work you are considering. The budget below is a starting orientation, not a checkout or final quote.

PROJECT SCOPESELECT ONE OR MORE
Combined starting budget$0

Final pricing depends on users, devices, locations, platforms, timing, and technical complexity.

EMAILoperations@grythenasystems.com ADDRESS408 Highland Ct, Iowa City, IA 52240 PHONE+1 702 707 6679